Fraud prevention is often discussed as a technology problem.
Buy another platform. Add another score. Insert another check. Produce another dashboard.
After more than 25 years working across fraud investigation, prevention and risk management, I have seen the same uncomfortable truth repeatedly: a fraud tool only becomes a control when an organisation knows what decision it is meant to change.
That matters now. UK Finance reported that criminals stole £1.28 billion through payment fraud in 2025, four per cent more than the previous year. At the same time, the UK's failure to prevent fraud offence has been in force since 1 September 2025, increasing the pressure on large organisations to demonstrate reasonable fraud-prevention procedures.
The answer is not to reject technology. It is to stop treating technology as the complete strategy.
The fraud problem is changing faster than the buying cycle
Fraudsters do not need to respect departmental boundaries, procurement processes or annual planning cycles. They look for the weakest point in a journey and adapt when controls move.
Artificial intelligence has increased the speed at which convincing identities, documents, messages and application variations can be produced. The underlying problem, however, is older and more familiar: organisations still collect signals without always joining them to a clear decision.
A name passes one check. A document passes another. An OTP reaches the mobile number supplied by the applicant. Each result may be technically correct, while the complete journey still deserves closer attention.
This is why fraud prevention cannot be measured by the number of systems installed. It should be measured by whether the organisation can answer four questions:
- What risk are we trying to identify?
- At what exact moment can we still change the outcome?
- Who owns the decision when a warning appears?
- Can we later explain what was known and why the decision was made?
If those answers are unclear, adding more technology can create more noise rather than more control.
Regulation has made governance part of fraud prevention
The UK Government's failure to prevent fraud guidance is important because it moves the conversation beyond detection alone.
For organisations within scope, the issue is not simply whether fraud occurred. It is whether reasonable prevention procedures existed around fraud committed by an associated person for the organisation's benefit.
That brings senior leadership, risk assessment, proportional controls, communication, monitoring and review into the same conversation.
Buying a fraud product can support that framework, but the invoice is not evidence that the framework works.
An organisation still needs to show:
- Which fraud risks it identified
- Why particular controls were selected
- Where those controls operate in the journey
- How exceptions and alerts are handled
- Who can change the rules
- What evidence is retained
- How outcomes feed back into future controls
The technology should serve the procedure. The procedure should not be reverse-engineered around whichever product was bought most recently.
The best fraud control is not the one with the most impressive dashboard. It is the one placed early enough to change the outcome and clear enough to be explained afterwards.
Start with the decision, not the data
Before introducing a new signal, define what could happen when it returns.
For example, if an applicant's mobile number shows recent SIM activity, what does that mean in this particular journey?
It may mean:
- Continue normally because the action is low risk
- Request independent step-up verification
- Delay a sensitive account change
- Route the case for review
- Compare the signal with account, device or transaction history
Recent SIM activity is not proof of fraud. People replace devices, change SIMs and move networks legitimately. The value of the signal depends on timing, context and consequence.
The same principle applies to identity matching. An OTP confirms that somebody can receive a code at that moment. It does not necessarily establish that the submitted name, address, postcode and date of birth align with information associated with the actual mobile number being used.
Mobile KYC can add that separate identity-alignment signal. Trust Score can add carrier-derived context such as recent SIM activity, number tenure, line type and other available network indicators.
Neither product should make the final decision. The organisation should decide how those signals affect its own journey.
Put controls where they can still prevent loss
Many controls are applied after expensive work has already begun.
An application may already have triggered identity checks, credit searches, document verification, manual review or call-centre activity before the mobile number is assessed.
That may be the right design for some journeys. For others, an earlier Step 0 mobile-risk check can provide useful context before further cost and operational time are committed.
The point is not that every customer should face every check. It is that the organisation should know why a control sits where it does.
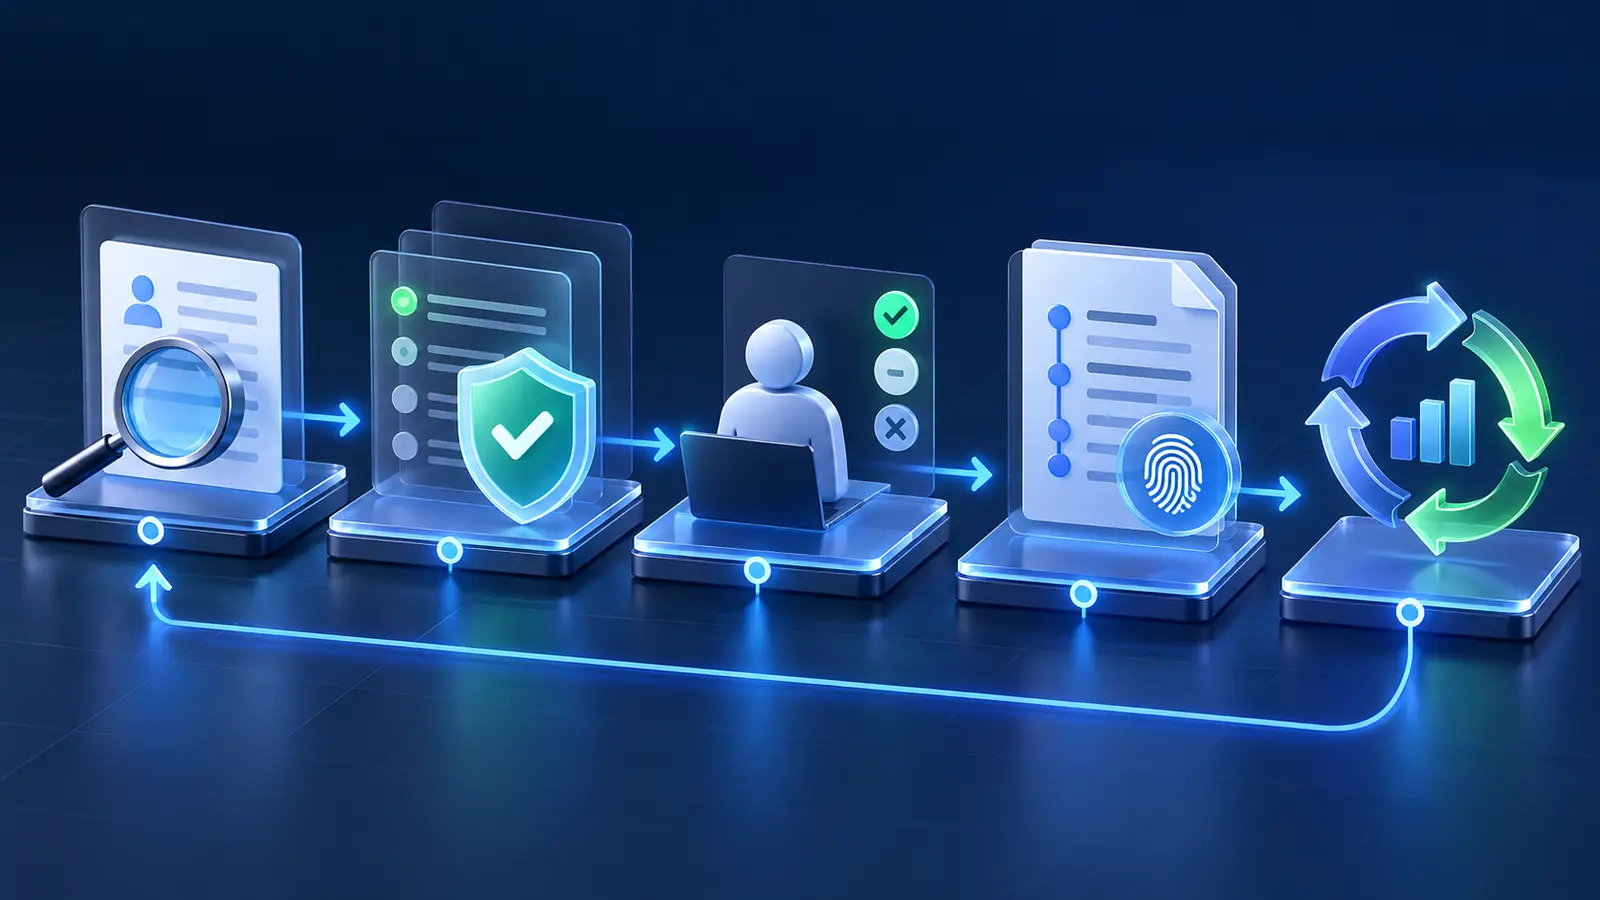
A practical control map should connect:
- The fraud scenario
- The point of exposure
- The available signal
- The permitted response
- The owner of that response
- The evidence retained afterwards
When those elements are connected, technology becomes part of an operating model rather than an isolated lookup.
Explainability matters before and after the decision
Fraud teams need more than a red, amber or green result.
They need to understand which indicators contributed to the outcome. Operations teams need clear escalation instructions. Compliance teams need evidence of the control. Customers need a fair route through when a legitimate event creates an unusual signal.
That is why reason codes matter. They allow a score or alert to be traced back to the indicators behind it rather than treated as an unexplained instruction.
The same principle applies to the audit trail. A useful record should show what check was run, when it was run, the processing context and the evidence returned at that point in time.
TDS Risk connects eligible checks to TDS Audit and Risk Recall so authorised users can reference the original verification evidence later. This does not replace the customer's own lawful-basis assessment, fraud policy or decision record. It strengthens the evidence available to support them.
Human judgement is not a design failure
Automation is valuable when the organisation understands what it is automating.
Low-risk journeys may continue without interruption. Defined combinations of signals may trigger another check. Higher-risk or unusual cases may be referred to a trained person.
That is not a weakness in the system. It is often the correct application of proportional control.
The failure occurs when staff receive alerts without knowing what they mean, customers are blocked because of one ambiguous indicator, or nobody owns the outcome once the technology has responded.
Rule Studio can help organisations test their own thresholds and combinations of mobile signals. But the quality of those rules still depends on the fraud scenarios, customer impact and escalation process established by the organisation.
Build the feedback loop
A fraud strategy cannot remain static while criminals continue testing it.
Controls should be reviewed against confirmed fraud, false positives, customer complaints, abandoned journeys and operational cost. A signal that looked important during design may prove less useful in practice. Another may become significant only when combined with a particular source, action or customer behaviour.
The feedback loop should ask:
- Which alerts changed a decision?
- Which rules created unnecessary friction?
- Which losses passed through without warning?
- Are particular channels or lead sources deteriorating?
- Do teams respond consistently to the same evidence?
- Can management see whether the control is improving?
This is where monitoring, smart alerts and webhook delivery become operationally useful. They help move relevant changes and audit events into the systems and teams that need to act on them. They still need an owner, a response and regular review.
What good fraud prevention looks like
Good fraud prevention is rarely one dramatic intervention.
It is a series of proportionate controls placed at the moments that matter. It combines reliable signals with documented rules, trained people, clear ownership and evidence that can be examined later.
Technology absolutely belongs in that model. It can provide speed, consistency and information that people cannot obtain manually at the point of decision.
But it cannot decide the organisation's risk appetite, create accountability or build a culture where concerns are raised and acted upon.
Do not ask only what the tool can detect. Ask where it operates, what decision it changes and what evidence remains.
That is the difference between owning fraud technology and operating a fraud-prevention strategy.
See how TDS Risk provides carrier-derived signals, reason codes and auditable evidence without making the final decision.
Explore explainable mobile risk controls ->Frequently asked questions
If it's not here, ask us directly — we reply within one UK business day.