A mobile number is often treated as a contact field. A business collects it, sends an OTP and moves on.
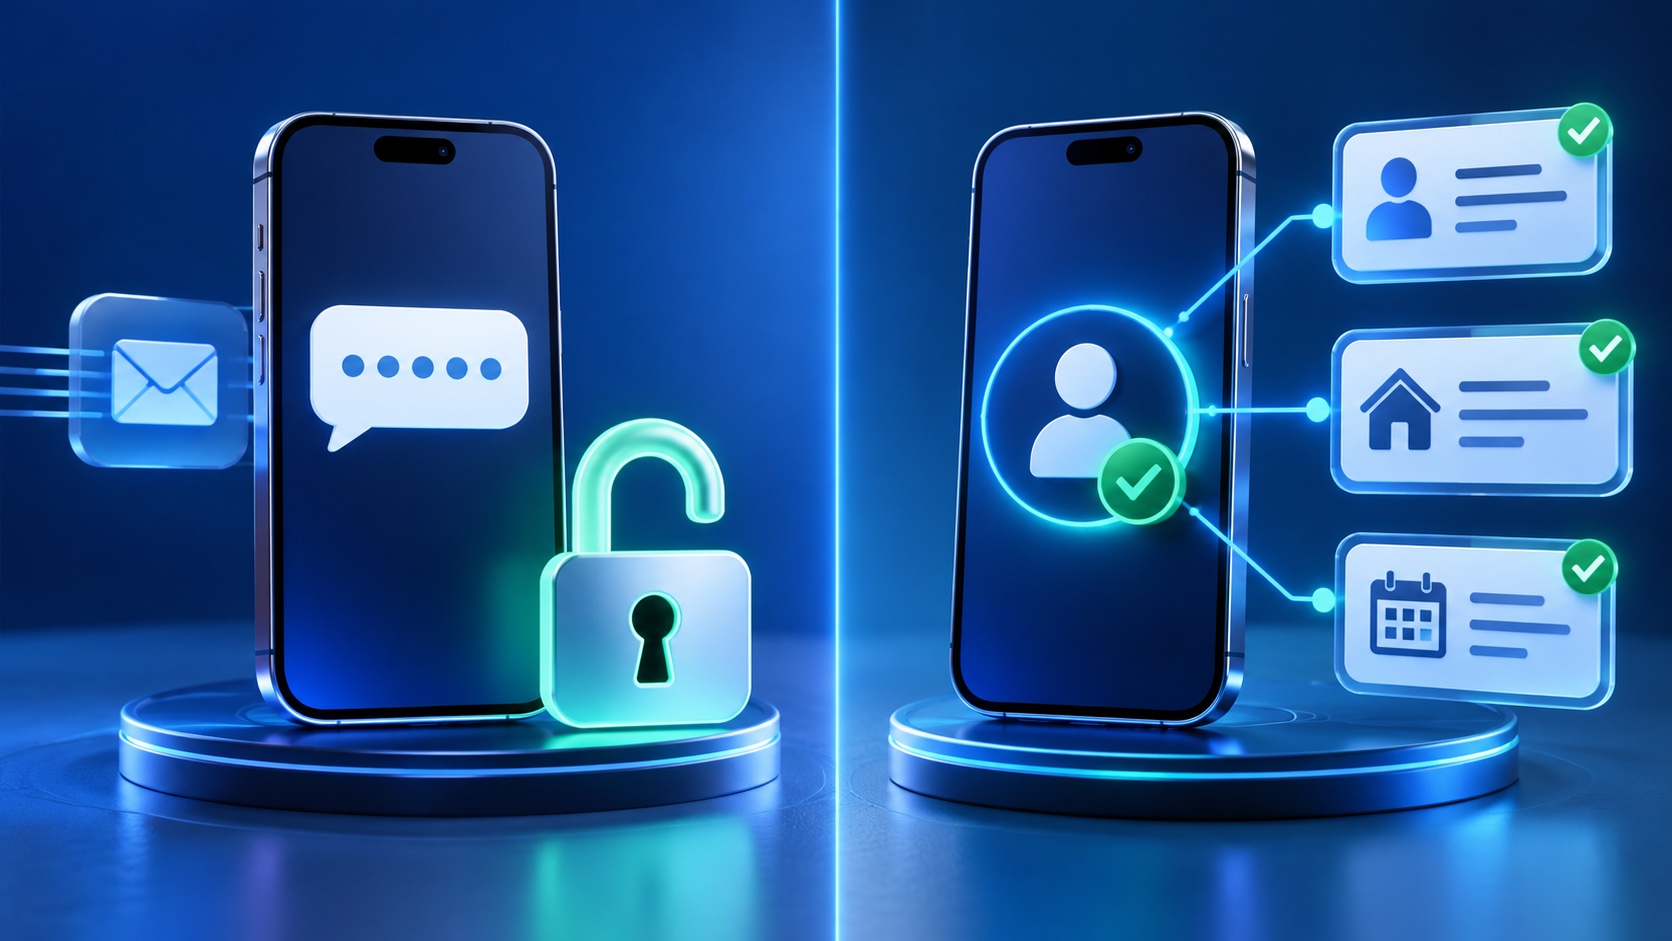
But an OTP and a Mobile KYC check answer different questions. An OTP can show that somebody can receive a code sent to the number at that moment. A Mobile KYC API checks whether the name, address and date of birth submitted in the journey match carrier-held information associated with the exact mobile number entered.
That distinction matters when somebody uses a number they control but submits another person's identity details. The OTP can succeed because the applicant receives the code. Mobile KYC can still surface that the identity details and the number do not align.
What is Mobile KYC?
Mobile KYC is a carrier-derived identity-matching check. It compares personal information supplied by an applicant with corresponding information associated with the mobile number in mobile network operator records.
With TDS Risk Mobile KYC, the returned result shows match information for the submitted name, address and date of birth. This helps a business assess whether the identity presented belongs with the number actually being used in the application.
It does not mean the network has confirmed who is physically holding the device, and a match does not prove that an application is genuine. It answers a narrower but commercially useful question: do the submitted identity details match the carrier-held information linked to this number?
Why an OTP does not match identity to the number
An OTP tests access to a communication channel. If somebody receives and enters the code, the business knows the code reached a channel they could access at that time.
It does not establish that the name, address or date of birth on the application belongs to the customer associated with the number.
An applicant can control the number, pass the OTP and still submit identity details that do not match the carrier-held record behind it.
Consider an online loan application using stolen personal details. The applicant enters their own mobile number, receives the OTP and passes that stage. A Mobile KYC check can compare the stolen name, address and date of birth with the carrier-held details associated with the applicant's number. Any mismatch becomes evidence the lender can handle within its own policy.
How does a Mobile KYC API work?
- The applicant provides a mobile number plus the name, address and date of birth needed for the check.
- The business sends those details securely to the API for its declared purpose.
- The submitted attributes are compared with the relevant carrier-held information associated with that number.
- The API returns match information for each supported attribute.
- The business applies its own rules: continue normally, request further evidence, use step-up verification or refer the application for review.
This makes Mobile KYC useful alongside existing fraud, identity, credit and compliance checks rather than as a replacement for them. Developers can review the TDS Risk quickstart guide before integrating the check.
What details can Mobile KYC match?
TDS Risk Mobile KYC returns granular match information for:
- Name
- Address
- Date of birth
The important part is the relationship. These attributes are not merely checked in isolation; they are compared with information associated with the specific number entered in the customer journey.
A business can therefore see which details align and which do not instead of treating a successful OTP as if it verified the whole identity. Results must still be interpreted in context because formatting, incomplete information or legitimate record differences may affect a match.
Mobile KYC, OTP verification and Trust Score
These checks can work together, but they are not interchangeable.
OTP verification
Shows that somebody can access a communication channel associated with the number at that moment. It does not compare identity attributes with carrier records.
Mobile KYC
Checks whether the submitted name, address and date of birth match carrier-held information associated with the number provided.
TDS Risk Trust Score
Trust Score assesses carrier-derived mobile risk signals such as recent SIM activity, number tenure, line type, ownership stability and network information. Trust Score assesses number risk; Mobile KYC compares identity details associated with the number.
Document or full identity verification
Uses documents, biometrics, databases or other evidence to complete the checks required by the business. Mobile KYC adds an earlier carrier-derived identity match but does not replace required due diligence.
Where should Mobile KYC sit in the journey?
If the number and identity details are collected at the beginning of an application, Mobile KYC can be used at Step 0, before the business commits to more expensive checks or manual work.
A lender might use it before ordering a credit search. An insurer might use it during a quote or policy application. A lead buyer might check whether submitted identity details align before paying to route or call the lead. An account provider might use it before opening an account or enabling a sensitive change.
The match result should inform the next step rather than make the final decision. The relevant industry examples are covered across the TDS Risk use-case pages.
Why does matching the actual number matter?
Fraudsters do not need to enter the victim's phone number. They can enter a number they control, receive the OTP themselves and still use stolen or manipulated identity information elsewhere in the application.
Mobile KYC closes that gap by checking whether the personal details submitted belong with the number used. That gives fraud and compliance teams a clearer reason to allow the normal journey, request more evidence or review the application.
Businesses considering the commercial placement of the check can model their volumes and downstream costs using the TDS Risk ROI calculator.
What should a good Mobile KYC response include?
A useful implementation should return more than one unexplained outcome. It should provide:
- Match information for each supported identity attribute
- A unique request identifier
- The time of the check
- A consistent response structure
- Clear handling for unavailable or inconclusive attributes
- An associated audit record
Every TDS Risk check is linked to an audit record so the request and returned result can be referenced later. The platform's wider controls are described on the security and compliance page.
How TDS Risk Mobile KYC works
TDS Risk Mobile KYC checks the submitted name, address and date of birth against carrier-held information associated with the mobile number provided. It operates across Vodafone, EE, Virgin Media O2 and Three.
Mobile KYC costs £0.45 per check excluding VAT. There are no contracts, minimum volumes or setup fees, and prepaid credit does not expire. Full commercial terms are shown on the TDS Risk pricing page.
The customer controls its own policy and final decision. TDS Risk supplies the carrier-derived match evidence and an auditable record of the check.
Match the identity to the number being used
An OTP can show access to a number. Mobile KYC checks whether the applicant's name, address and date of birth match the carrier-held information linked to that number.
That extra comparison helps businesses identify discrepancies earlier and choose the appropriate verification route before unnecessary downstream cost is incurred.
Match the submitted name, address and date of birth to carrier-held information linked to the number used.
Explore Mobile KYC API →Frequently asked questions
If it's not here, ask us directly — we reply within one UK business day.